Malware analysis in Android
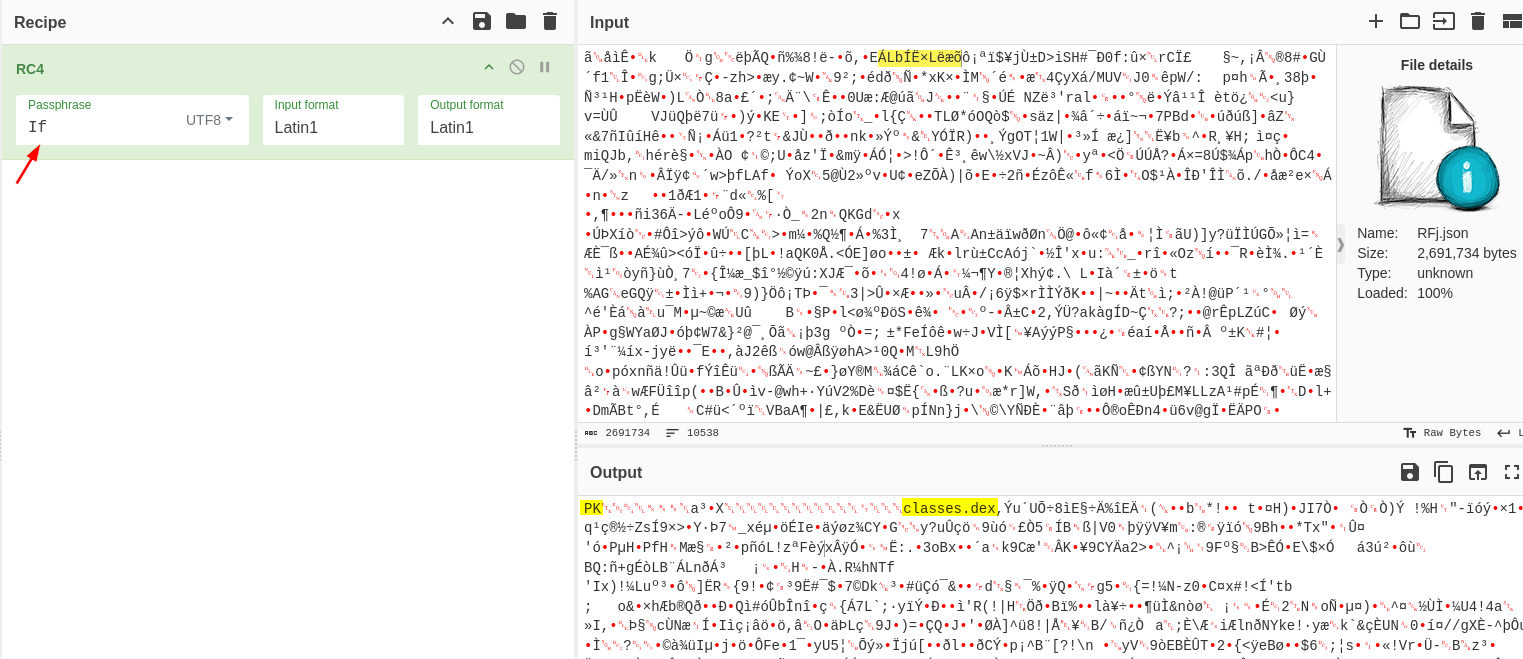
Reverse engineering of a packed Android sample from the GodFather infostealer family: unpacking, C2 address recovery, victim registration and encrypted communications.
Reverse engineering of a packed Android sample from the GodFather infostealer family: unpacking, C2 address recovery, victim registration and encrypted communications.
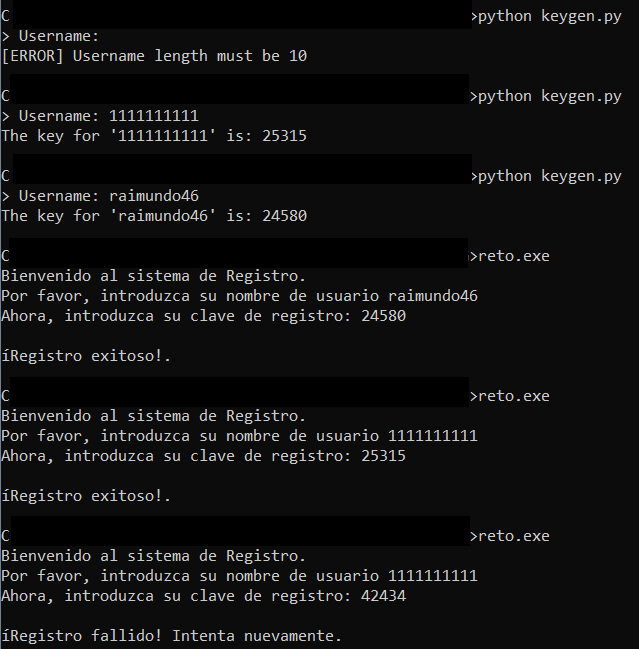
Static analysis with IDA Freeware of a PE32 crackme written in C: how the username and key validation works, and a Python keygen that generates valid keys.