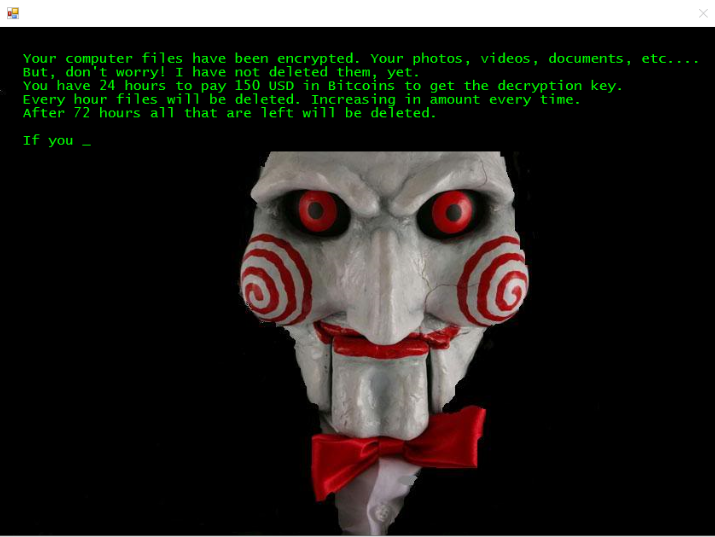
Malware Analysis of Jigsaw Ransomware
Static and dynamic analysis of a Jigsaw ransomware sample: infection, persistence, encryption and extortion, with IoCs, YARA rules, security measures and a working decryptor.
Static and dynamic analysis of a Jigsaw ransomware sample: infection, persistence, encryption and extortion, with IoCs, YARA rules, security measures and a working decryptor.
Static and dynamic analysis of an Android application following the OWASP methodology, with a technical and executive report, CVSS scoring and mitigation recommendations.
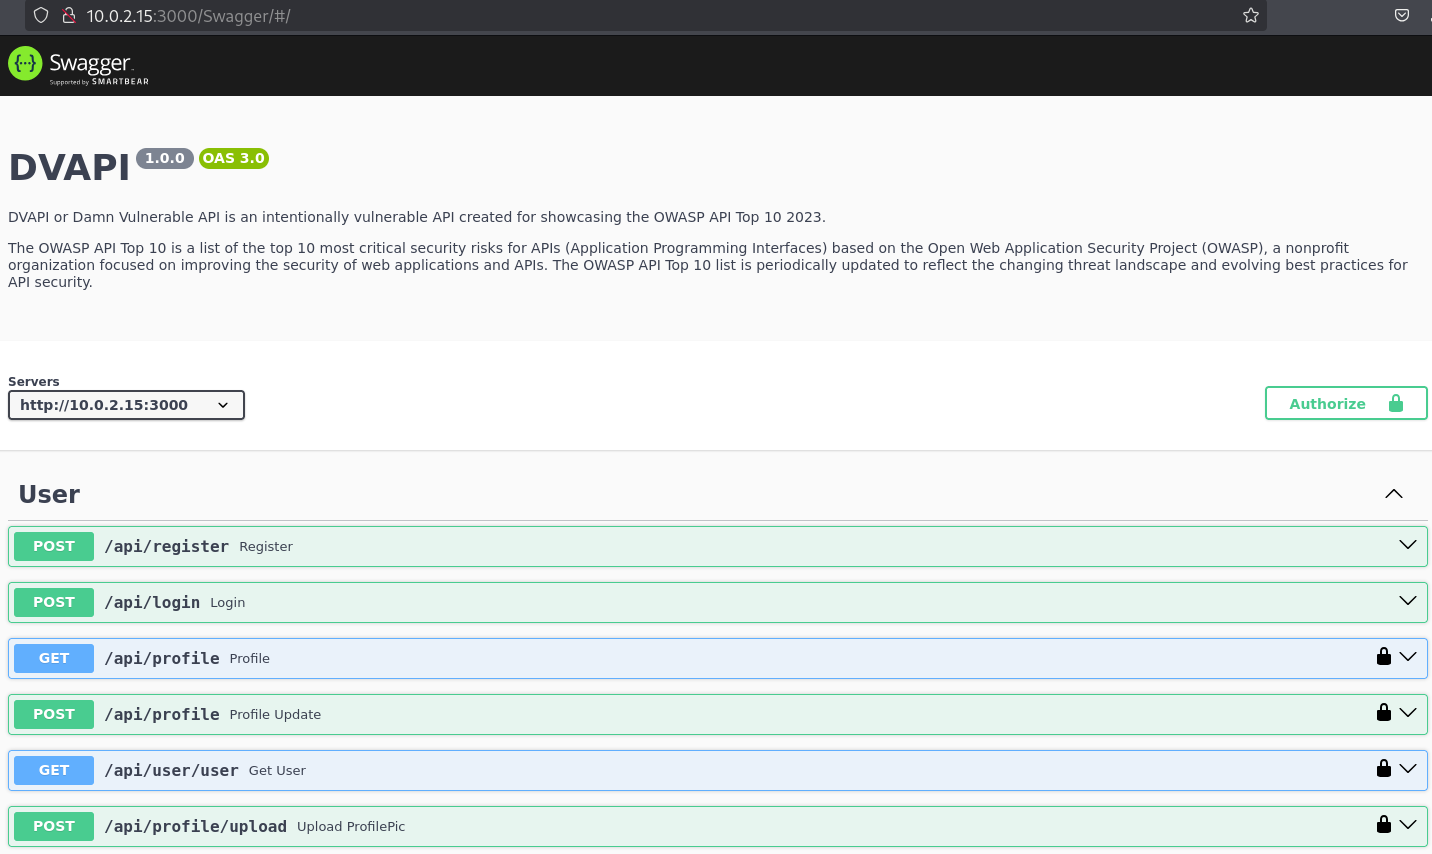
A hands-on walkthrough of the 10 most important API vulnerabilities according to OWASP: what they are, how to detect them, how to exploit them in a controlled environment (DVAPI) and, above all, how to mitigate them.
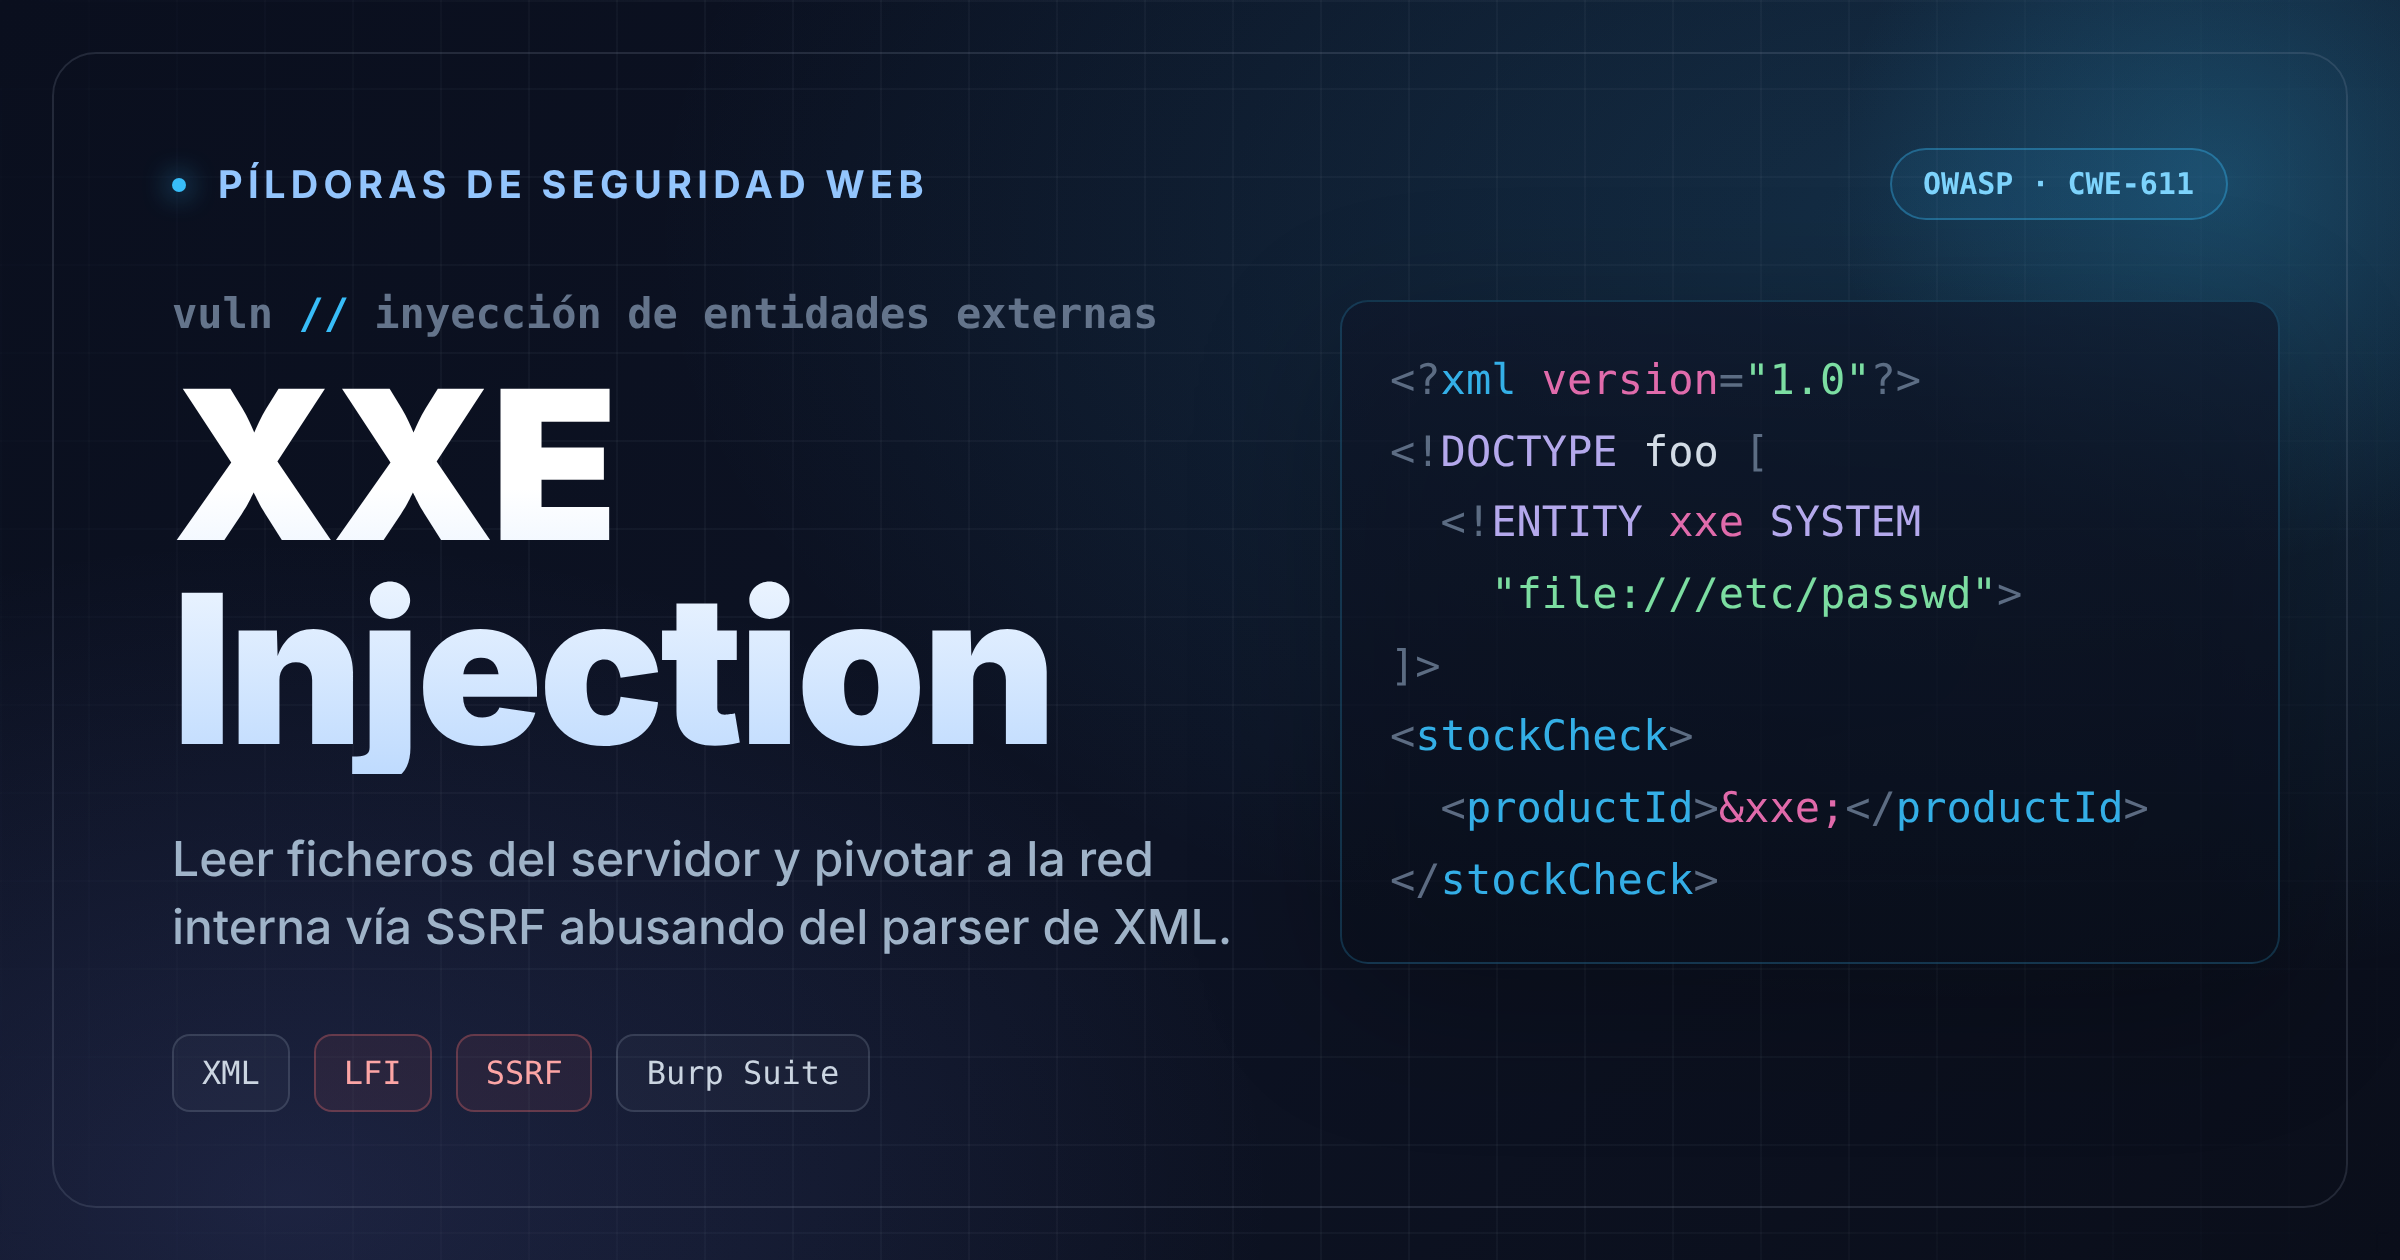
What XXE (XML External Entities) injection is, how to detect and exploit it to read files from the server and perform SSRF, and how to mitigate it.
Third and final installment of the series. We impersonate a Domain Admin with runas, mimikatz and Rubeus, perform lateral movement to the domain controller with Metasploit, and close with a reflection on Kerberoasting.
Second installment of the series. We enumerate the CAPSULE.CORP domain with PowerView, identify accounts with sensitive attributes and exploit them with AS-REP Roasting and Kerberoasting using Impacket and hashcat.
First installment of the Active Directory pentesting series. A lab is built from scratch with VirtualBox, a domain controller is deployed, users are created and vulnerable configurations are seeded to practice attacks.
Basic analysis of a Lumma Stealer sample disguised as KMSPico.exe using VirusTotal, ANY.RUN and Joe Sandbox: behavior, TTPs, IoCs and security measures.
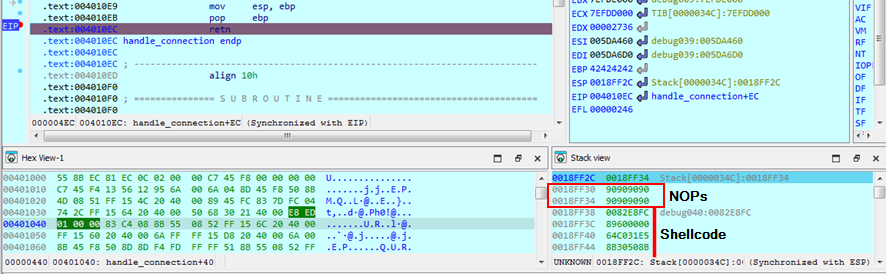
Step-by-step reverse engineering and exploitation of a Buffer Overflow in a Windows echo server, bypassing the canary cookie and using ROP to achieve arbitrary code execution.
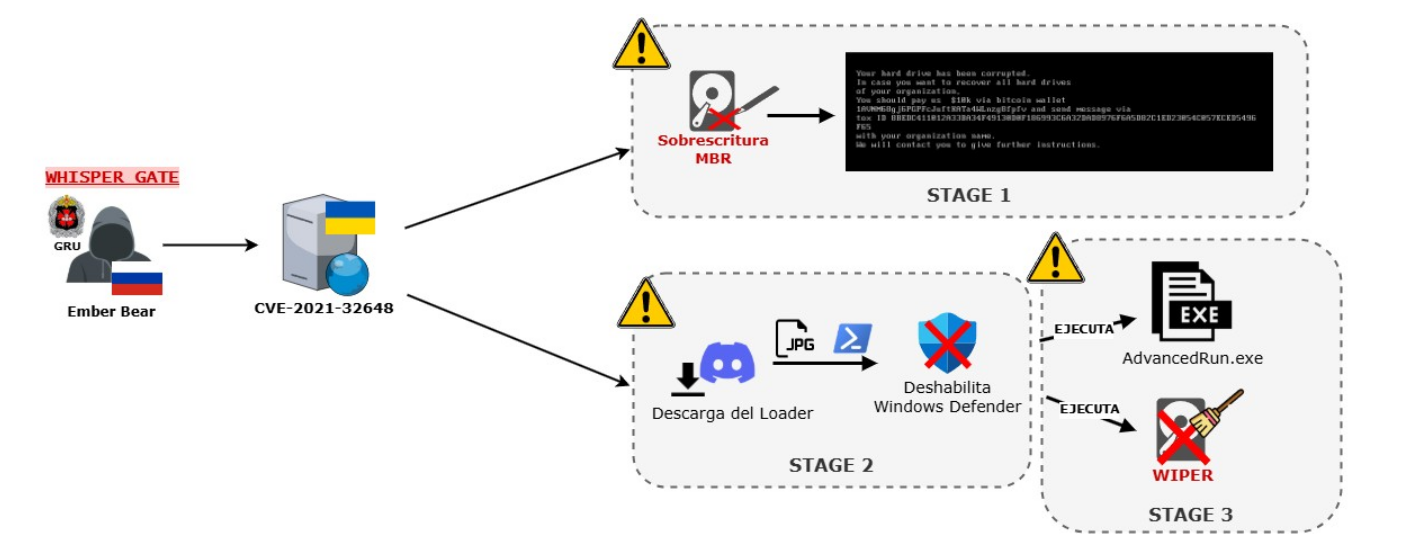
Threat Intelligence report on the WhisperGate wiper with an executive summary and a technical analysis: Cyber Kill-Chain, MITRE ATT&CK TTPs, IoCs and security measures.