WhisperGate Threat Context Report
Threat Intelligence report on the WhisperGate wiper with an executive summary and a technical analysis: Cyber Kill-Chain, MITRE ATT&CK TTPs, IoCs and security measures.
Introduction
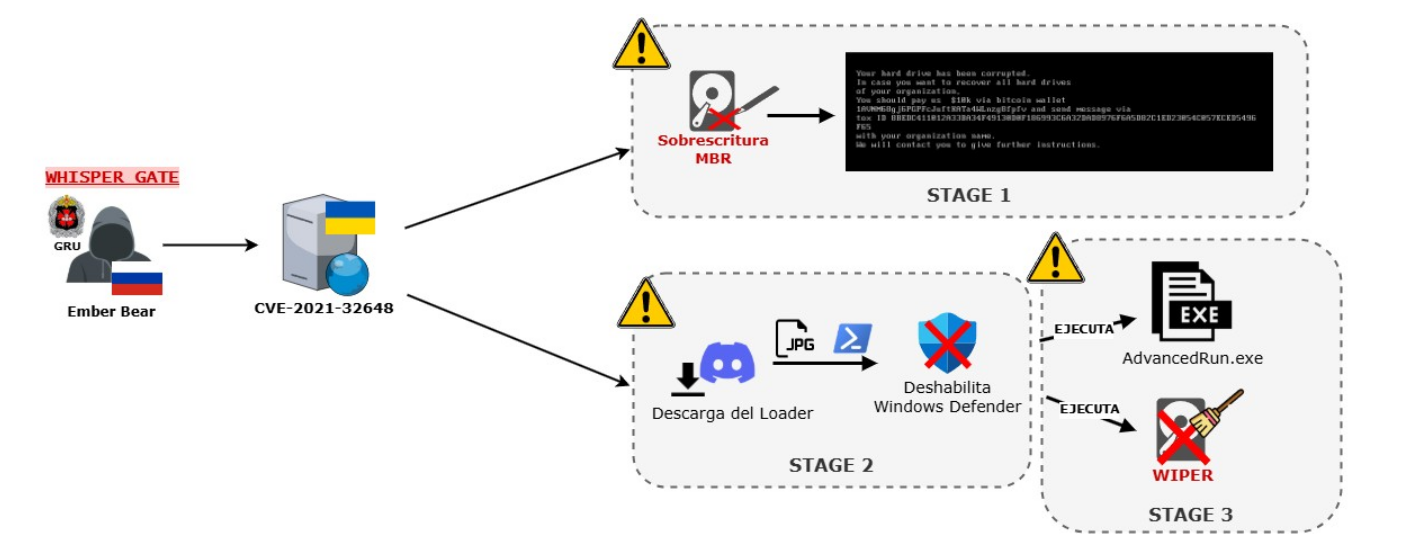
On January 13, 2022, dozens of Ukrainian government systems woke up to a ransom note on their screens. But it was not ransomware: WhisperGate pretended to be one while overwriting the MBR and destroying its victims’ files, with no real chance of recovery. A disguised wiper, launched on the eve of Russia’s invasion of Ukraine.
This report stems from a simple question: what does a defense team need to know to understand, detect and stop a threat like this? The answer is structured into two reading levels, aimed at different audiences, within a single document.
Project description
The work is a Threat Intelligence report on WhisperGate that combines an executive summary with a technical analysis:
- Executive level: what happened, who is affected, what the business impact is and which decisions follow, with no technical background required.
- Technical level: how the malware operates at each stage of the attack, what capabilities it has and what traces it leaves on compromised systems.
The report is structured around four deliverables:
- Cyber Kill-Chain description: a walkthrough of the attack stages, from initial access to destructive impact, to understand where and when the chain can be broken.
- TTPs (MITRE ATT&CK): a mapping of the observed tactics, techniques and procedures, useful to compare the behavior with other actors and build detections.
- IoC extraction: indicators of compromise (hashes, domains, paths and artifacts) ready to be loaded into monitoring and threat hunting tools.
- Security measures proposal: prioritized preventive, detective and response controls to reduce exposure to similar threats.
All of this from a Blue Team perspective: not only analyzing the malware, but turning that analysis into actionable information.